
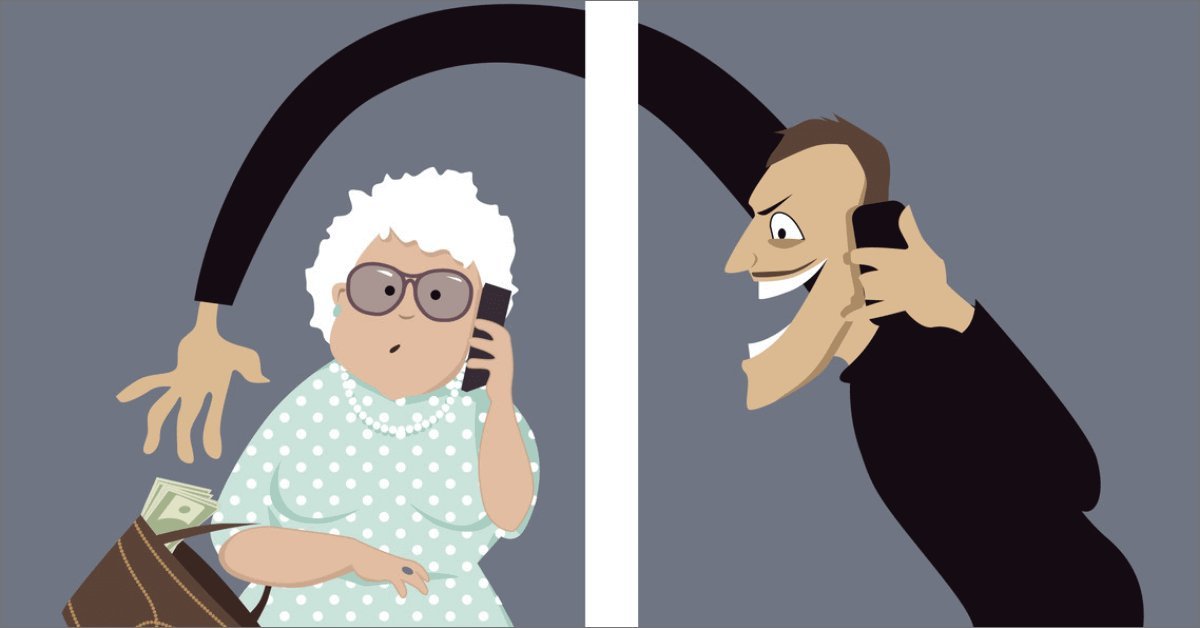
You cloned your voice for legitimate work — now that model is a digital key to your identity. Learning how to prevent misuse of your cloned voice is essential security hygiene in 2026, whether you’re a creator, executive, or just someone who’s recorded a lot of audio.
How to Prevent Misuse of Your Cloned Voice
A voice clone enables: impersonation scams targeting your family and colleagues, fake endorsements and statements, unauthorized commercial use, and social engineering of your organization. Executives are prime targets — one convincing “urgent wire transfer” call in a CEO’s voice can cost millions. Your voice model files deserve the same protection as passwords.
Securing your voice models and data
- Keep model files private and encrypted. Never share raw voice model files; store them encrypted with access limited to you.
- Use reputable platforms with consent verification (ElevenLabs requires verification for voice cloning) — avoid shady tools that clone anyone from seconds of audio with no checks.
- Limit training-data exposure. Every public recording is potential training data. You can’t go silent, but avoid posting clean, isolated vocal recordings (dry acapellas, voice notes) publicly.
- Use platform voice verification where offered — some services let you register your voice to block unauthorized cloning.
- Watermark AI-generated audio from your clone so legitimate outputs are distinguishable from fakes.
Monitoring for misuse
- Set up alerts: your name + “AI voice,” “voice clone,” “deepfake.”
- Brief your inner circle (family, assistant, finance team) on verification procedures — a family safe word defeats most impersonation.
- For executives: establish out-of-band verification for any unusual request (call back on known numbers; require video or in-person for large transfers).
- Monitor social platforms for impersonating accounts using your voice.
Legal protections (know your rights)
Protection is strengthening: Tennessee’s ELVIS Act explicitly protects vocal likeness; several states have digital-replica laws; the EU AI Act requires disclosure of AI-generated content; and right-of-publicity laws in many jurisdictions cover commercial voice misuse. Document your voice’s commercial value (bookings, endorsements) — it strengthens any claim. For serious misuse, consult a lawyer specializing in publicity rights or entertainment law.
If misuse happens: response plan
- Document everything — screenshots, URLs, timestamps, witnesses.
- Report to platforms — all major platforms have impersonation reporting; act fast.
- Issue a public denial if the fake is spreading — silence lets it grow.
- File reports with FTC/police for fraud; consult a lawyer for commercial misuse.
- Notify your circle so they don’t fall for follow-up attempts.
Enterprise voice security programs
For organizations, voice cloning threats require systematic defenses, not just individual caution. A solid program includes: verification protocols for sensitive actions (any voice instruction involving money, access, or data requires out-of-band confirmation — no exceptions, regardless of how senior the “caller” sounds), employee training (quarterly social-engineering exercises including voice-clone scenarios — people who’ve practiced resisting don’t panic), communication norms (established channels for urgent requests; anything arriving via unusual channels gets verified), and technical controls (call authentication where available, anomaly detection on financial systems).
Executive protection deserves special attention: limit executives’ public voice exposure where practical, brief their families and assistants (attackers target the circle, not just the executive), and establish duress signals for truly sensitive operations. The cost of these measures is trivial compared to a single successful voice-clone fraud — which regularly runs into six or seven figures.
Staying ahead of the threat
The threat evolves — so should defenses. Track: FBI IC3 alerts on emerging voice-fraud tactics, CISA guidance on social engineering defenses, and your industry’s ISAC (Information Sharing and Analysis Center) for sector-specific threats. And run annual voice-security audits: test your verification protocols with simulated attacks, review who’s been briefed, update procedures. Security is a practice, not a product.
Personal voice security audit
Run this audit for yourself this week. Exposure: search your name + “podcast/video/interview” — how much clean public audio exists? Can you reduce it (friends-only settings, removing old voice notes)? Circle: have you briefed family on verification procedures? Is there a safe word? Accounts: do any use voice authentication? (Consider switching to app-based.) Monitoring: are alerts set up for your name + AI voice/deepfake terms? Response: do you know exactly what to do if misuse happens — who to call, where to report?
Thirty minutes, once a year. That’s the maintenance cost of voice security for most people. The threat is real but the defense is simple — exposure reduction, circle briefing, monitoring, response plan. Do the audit, fix the gaps, get on with your life. Security done right is boring, and boring is the goal.
Practical takeaway
- Treat voice models like passwords: encrypted, private, access-controlled.
- Set up monitoring alerts and brief your circle on verification.
- Know your legal rights — vocal likeness protection is growing.
- Have a response plan ready before you need it.
- Use consent-verified platforms; avoid no-check cloning tools.
Keep exploring
If you found this useful, these related guides go deeper:

1 Comment